Cybersecurity
HollowByte: The 11-Byte Vulnerability Crippling OpenSSL and its Impact on Patch Management
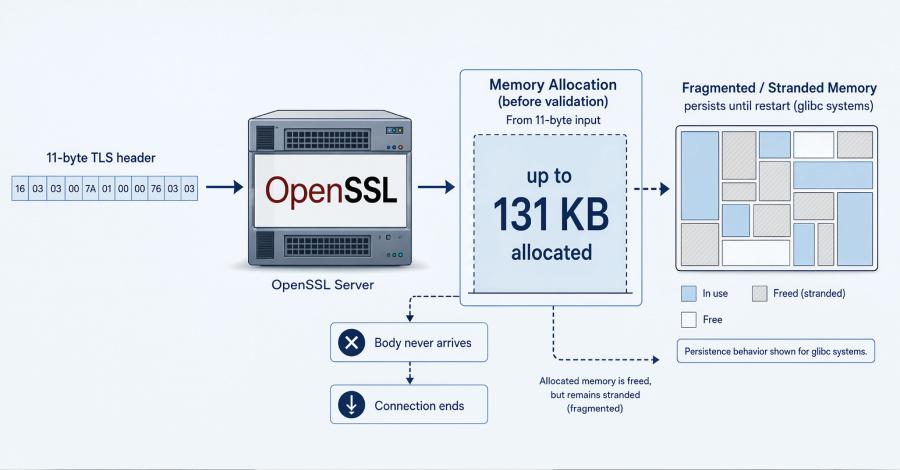
A critical vulnerability, dubbed HollowByte, allows unauthenticated attackers to induce a Denial-of-Service (DoS) condition in OpenSSL servers using a mere 11-byte payload. This attack can freeze up to 131 KB of memory per request on glibc-based systems, persisting until the affected process is restarted. OpenSSL implemented a fix in June 2026 without a CVE, public advisory, or changelog entry, creating significant challenges for security management and critical patch identification.
Carlos "Emérito" López Lovera