Introduction to HollowByte: A Low-Resource DoS Vector
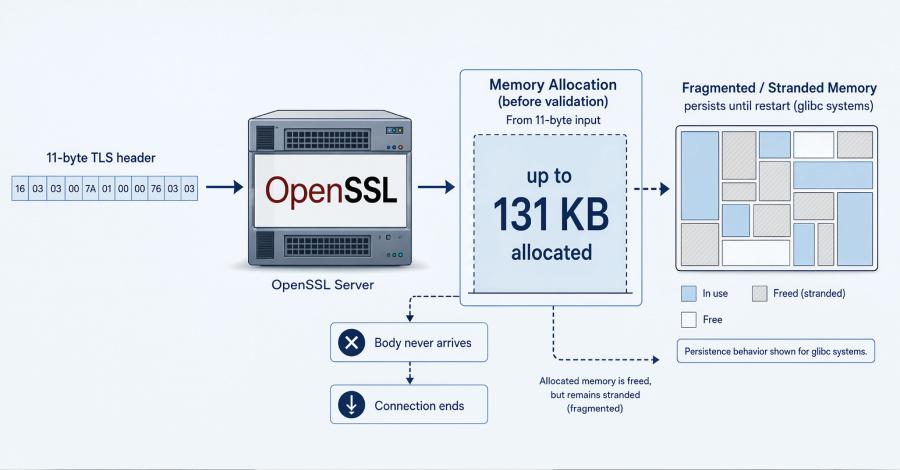
The vulnerability dubbed HollowByte poses a significant threat to the availability of services utilizing the OpenSSL library. This flaw allows unauthenticated attackers to induce a Denial-of-Service (DoS) condition on vulnerable servers. The attack mechanism relies on manipulating TLS requests with a minimal payload of just 11 bytes. On operating systems using glibc, each of these malicious requests can cause the server to reserve up to 131 KB of memory, which remains allocated and is not released until the OpenSSL process is restarted.
Technical Mechanism of the Vulnerability
The technical core of HollowByte lies in how OpenSSL handles incomplete TLS messages during the handshake phase. When an OpenSSL server receives a truncated or malformed TLS request, particularly one that does not complete the handshake, the system allocates memory buffers to process the incoming message. In HollowByte's case, an 11-byte payload is sufficient to trigger this memory allocation without the message completing. The peculiarity of glibc-based systems is that this allocated memory is not automatically released if the handshake process does not complete or is abnormally interrupted. Consequently, multiple 11-byte requests can accumulate 131 KB memory allocations each, progressively exhausting the server's available resources. This process continues until the OpenSSL process depletes system memory or reaches configured limits, necessitating a manual or automatic restart of the service to free up the retained resources.
Operational and Economic Implications
The implications of HollowByte are directly proportional to OpenSSL's reliance in critical infrastructure. Operationally, a successful DoS attack results in service unavailability, severe performance degradation, or the collapse of the affected process. This directly impacts web servers (HTTPS), VPNs, email services (SMTPS, IMAPS), and any other application using OpenSSL for secure communications. From an economic perspective, service disruption translates into revenue losses, especially for e-commerce platforms, financial services, or cloud service providers. Recovery costs include technical staff time to identify the cause, restart services, and apply patches. Additionally, the organization's reputation can be compromised by service interruption, affecting customer and business partner trust. The ability of an 11-byte attack to cause such disruption highlights a low-cost vulnerability for the attacker but a high-impact one for the victim.
Challenges in Patch Management and Transparency
A critical aspect of the HollowByte vulnerability is how OpenSSL managed its disclosure and fix. The patch implementation in June 2026 occurred without a Common Vulnerability Identifier (CVE), without a formal security advisory, and without an explicit entry in the changelog. This lack of transparency creates a significant challenge for security teams and system administrators. Without a CVE, organizations lack a standard reference to identify the vulnerability, its severity, or its patching status. The absence of a formal advisory prevents monitoring systems and patch management tools from proactively alerting about the need for an update. This forces administrators to conduct manual audits or to update OpenSSL broadly without a clear understanding of the specific risk they are mitigating, potentially leading to delays in applying critical patches and increased exposure to attacks. This practice contrasts with industry standards for responsible vulnerability disclosure, which aim to balance the need to protect users with the need to provide clear and actionable information for remediation.
Monitoring and Resilience Management
The primary mitigation for HollowByte is the application of OpenSSL versions that include the fix, available since June 2026. System administrators must ensure that all OpenSSL instances in their infrastructure are updated to the latest versions. Beyond patching, the HollowByte incident underscores the need for proactive and robust monitoring of server resources, especially memory usage. Detecting anomalous memory allocation patterns can be an early indicator of a DoS attack attempt. Transparency in critical vulnerability disclosure is fundamental for the resilience of global digital infrastructure. The HollowByte incident highlights the tension between proactive security and information management in the open-source ecosystem, and emphasizes the importance of a patch management strategy that considers both regular updates and the ability to react to threats with limited disclosure.


