Skip to content

Cybersecurity News

Explore the latest news, analysis, and updates about Cybersecurity.

Cybersecurity

Analyzing Cybersecurity Strategy in Enterprise AI Adoption

A Dark Reading virtual event will address building a robust security strategy for artificial intelligence in the enterprise, highlighting growing concerns over emerging attack vectors and the need for dedicated AI protection frameworks beyond traditional cybersecurity practices.

Carlos "Emérito" López Lovera
Cybersecurity

Cloud Cybersecurity: Protecting Business Assets in the Age of AI

A forthcoming virtual event will address essential strategies for protecting assets in enterprise cloud environments, highlighting the critical intersection with artificial intelligence and the security implications this technology introduces into cloud infrastructure.

Carlos "Emérito" López Lovera
Cybersecurity

Critical Vulnerability in Ruby on Rails Active Storage Allows Remote Code Execution

Ruby on Rails has patched critical vulnerability CVE-2026-66066 in its Active Storage component, with a CVSS score of 9.5. This flaw allowed unauthenticated attackers to read arbitrary files and escalate to potential remote code execution (RCE) in Rails applications, impacting image processing.

Carlos "Emérito" López Lovera
Cybersecurity

AI Boosts Cryptocurrency Scams: Solana Foundation CISO's Warning

Michael Coates, the new CISO of Solana Foundation, has warned that artificial intelligence (AI) is significantly increasing the sophistication of cryptocurrency scams. He anticipates that AI-related vulnerabilities and the creation of fake identities will drive the next phase of blockchain security challenges.

Carlos "Emérito" López Lovera
Cybersecurity

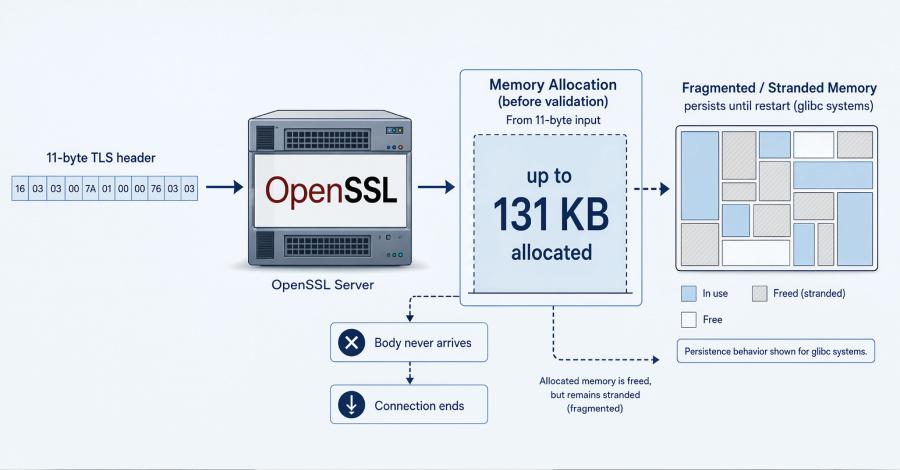
HollowByte: The 11-Byte Vulnerability Crippling OpenSSL and its Impact on Patch Management

A critical vulnerability, dubbed HollowByte, allows unauthenticated attackers to induce a Denial-of-Service (DoS) condition in OpenSSL servers using a mere 11-byte payload. This attack can freeze up to 131 KB of memory per request on glibc-based systems, persisting until the affected process is restarted. OpenSSL implemented a fix in June 2026 without a CVE, public advisory, or changelog entry, creating significant challenges for security management and critical patch identification.

Carlos "Emérito" López Lovera
Cybersecurity

Microsoft Addresses Record Vulnerabilities with Two Actively Exploited Zero-Days

Microsoft has released a record-breaking security update, patching 622 vulnerabilities, including two zero-days actively being exploited. This number signifies a substantial increase from previous months, highlighting continuous pressure on the corporation's security posture and the urgent need for patch application.

Carlos "Emérito" López Lovera
Cybersecurity

Forg365: The New PhaaS Platform Using AI and AiTM to Compromise Microsoft 365

Forg365 has emerged as an advanced Phishing-as-a-Service (PhaaS) platform, specifically designed to steal Microsoft 365 credentials. It leverages techniques like Adversary-in-the-Middle (AiTM) and Device Code Phishing, augmented by artificial intelligence (AI) for lure generation, enabling it to bypass multi-factor authentication (MFA) and enhance attack effectiveness.

Carlos "Emérito" López Lovera
Cybersecurity

CISA Issues Critical Alert for Actively Exploited Vulnerabilities in Langflow and ColdFusion

The Cybersecurity and Infrastructure Security Agency (CISA) has issued urgent directives to U.S. federal agencies to patch two actively exploited vulnerabilities: one in the Langflow AI agent development framework and another of maximum severity in the Adobe ColdFusion platform. Both require immediate mitigation, with a deadline set for Friday, highlighting the exposure to significant risks in critical AI infrastructures and government web applications.

Carlos "Emérito" López Lovera