Skip to content

Cybersecurity News

Explore the latest news, analysis, and updates about Cybersecurity.

Cybersecurity

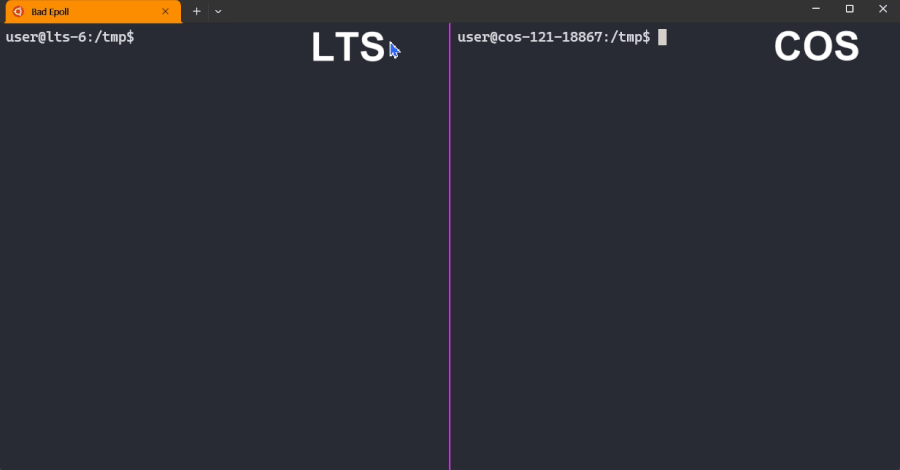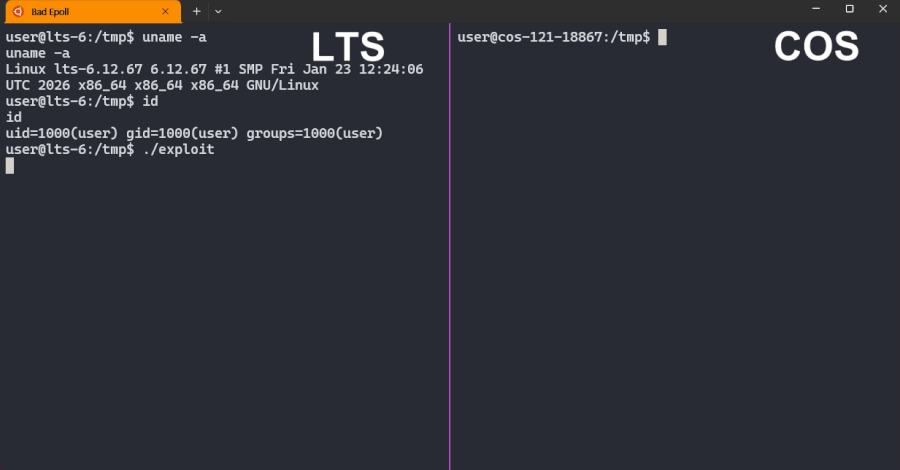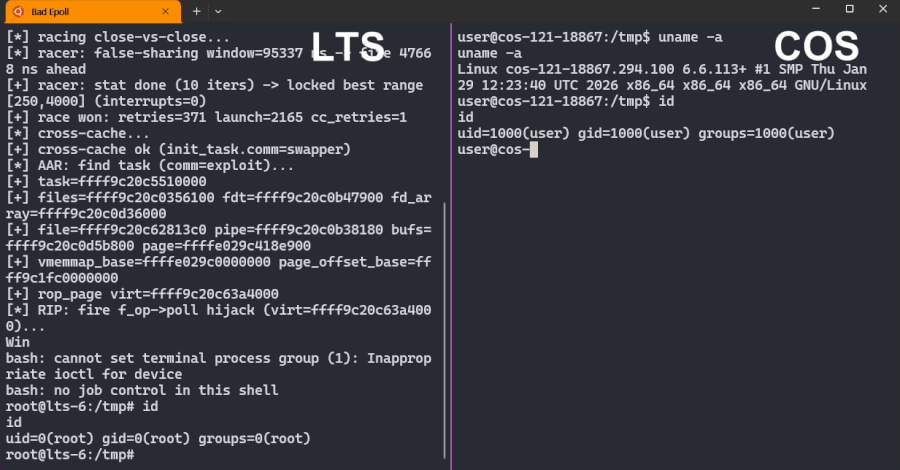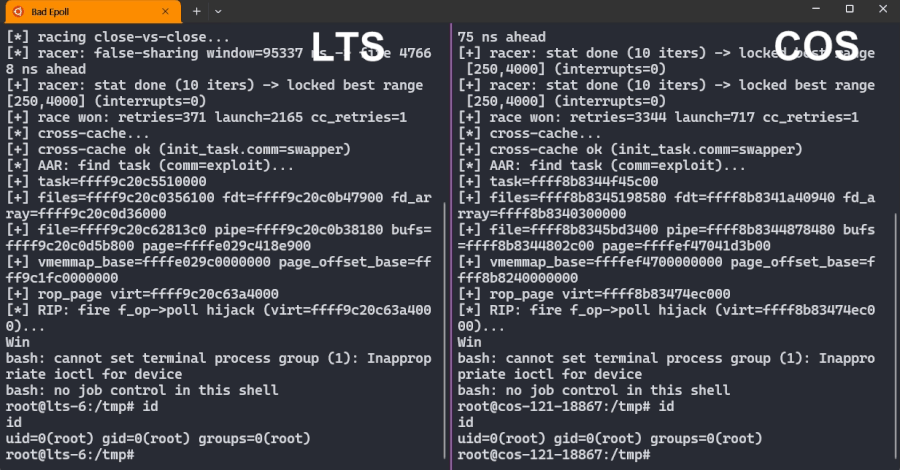
Critical 'Bad Epoll' Flaw in Linux Kernel: Analyzing Security Implications and Deployment

A privilege escalation vulnerability, identified as CVE-2026-46242 and dubbed 'Bad Epoll,' has been discovered in the Linux kernel. This flaw allows unprivileged users to gain root control over Linux systems, including desktops, servers, and Android devices. A fix has been released, making immediate patch deployment imperative to mitigate the risk of system compromise.

Carlos "Emérito" López Lovera
Cybersecurity

Armored Likho: Hybrid Threat Actor and Critical Infrastructure Exploitation

A previously undocumented threat actor, dubbed Armored Likho, has been identified as responsible for cyberattacks against government agencies and the power sector in Russia, Brazil, and Kazakhstan. The campaign employs BusySnake Stealer malware, demonstrating a hybrid strategy that combines financial motivation with a focus on critical infrastructure.

Carlos "Emérito" López Lovera
Cybersecurity

DirtyClone: Undetectable Privilege Escalation in the Linux Kernel and Its Implications

The DirtyClone vulnerability (CVE-2026-43503) is a privilege escalation flaw in the Linux kernel allowing local users to gain root access. Part of the DirtyFrag family, it undetectably rewrites executables in memory without leaving disk traces, complicating detection. With a CVSS score of 8.8, it marks the fourth critical Linux kernel vulnerability disclosed in the past six weeks.

Carlos "Emérito" López Lovera
Cybersecurity

Stealth Attack: Fileless Phantom Stealer Compromises Browser Credentials

Phantom Stealer malware operates 'fileless,' executing entirely in memory to evade traditional detection. This malicious software is designed to exfiltrate browser credentials, incorporating anti-analysis techniques that thwart identification and mitigation efforts. Its evasive nature poses a significant challenge to current cybersecurity defenses.

Carlos "Emérito" López Lovera
Cybersecurity

China-Nexus Actor Compromises U.S. Researchers' RedCAP Credentials for a Year

Google has revealed the disruption of an advanced cyberespionage campaign, attributed to a China-nexus actor, which operated undetected for a year. The operation compromised RedCAP (Research Electronic Data Capture) credentials from numerous U.S. research institutions, facilitating the exfiltration of sensitive data with strategic and economic implications.

Carlos "Emérito" López Lovera
Cybersecurity

AI Supply Chain Compromise: The Miasma Worm via ai-sdk-ollama

A recent software supply chain attack has been identified involving a trojanized npm package, `ai-sdk-ollama`. This malicious package distributes the self-replicating `Miasma` worm by exploiting the `binding.gyp` mechanism, highlighting critical vulnerabilities in open-source software dependencies, particularly within the growing AI development ecosystem.

Carlos "Emérito" López Lovera
Cybersecurity

The Evolution of Phishing: Lower Volume, Higher Risk Driven by AI

Phishing attack volumes have dropped by 20%, yet the overall risk has increased. Attackers are prioritizing quality over quantity, integrating Artificial Intelligence (AI) to enhance the sophistication and effectiveness of their campaigns, leading to higher mitigation costs and a re-evaluation of corporate cybersecurity strategies.

Carlos "Emérito" López Lovera
Cybersecurity

CISA Issues Urgent Directive Over Zero-Day Vulnerability Exploitation in Check Point VPNs

The Cybersecurity and Infrastructure Security Agency (CISA) has imposed a three-day deadline for U.S. federal agencies to mitigate a critical zero-day vulnerability in Check Point's remote access and mobile access VPN products. This vulnerability is actively being exploited by affiliates of the Qilin ransomware group, compromising the security of dozens of organizations and exposing critical systems to data exfiltration and operational disruption.

Carlos "Emérito" López Lovera
Cybersecurity

Dark Reading's 20th Anniversary: An Indicator of Maturity in Cybersecurity Information

Dark Reading's 'Name That Toon Contest' announcement marks its twentieth anniversary, signifying two decades of operation in cybersecurity. This milestone highlights the platform's consolidation as a relevant technical information source and its sustained influence in shaping industry discourse and trends. Such longevity in a dynamic field like cybersecurity demonstrates constant adaptation and validation of its editorial and economic model.

Carlos "Emérito" López Lovera
Cybersecurity

CISA Catalogs SolarWinds Serv-U Vulnerability as Actively Exploited

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added vulnerability CVE-2026-28318, affecting SolarWinds Serv-U, to its Known Exploited Vulnerabilities (KEV) catalog. This high-severity vulnerability (CVSSv3.1 score of 7.5) is actively being exploited by malicious actors to cause server crashes, emphasizing the critical need for immediate mitigation in corporate and government environments.

Carlos "Emérito" López Lovera
Cybersecurity

Dutch Operation Dismantles Massive Botnet: 17 Million Devices Compromised

Dutch authorities have successfully dismantled a massive global botnet comprising at least 17 million infected devices, including computers, tablets, smartphones, and IoT devices. The operation involved seizing over 200 servers linked to the botnet's infrastructure, which was associated with the Asocks proxy service, highlighting the escalating scale of cyber threats and the complexity of digital law enforcement operations.

Carlos "Emérito" López Lovera
Cybersecurity

Two Decades of Dark Reading: The Critical Evolution of Cybersecurity and Its Implications

Dark Reading's 20th anniversary marks a cybersecurity milestone, reflecting the sector's transformation from basic perimeter protections to advanced AI-driven architectures. This analysis details technical evolution, the multi-billion dollar economic impact of threats, and defensive strategies adapted to an expanding risk landscape.

Carlos "Emérito" López Lovera