Skip to content

Exploring #Kernel

Everything you need to know about Kernel. Read our latest news and technical analysis to understand its market impact.

Cybersecurity

Critical 'Bad Epoll' Flaw in Linux Kernel: Analyzing Security Implications and Deployment

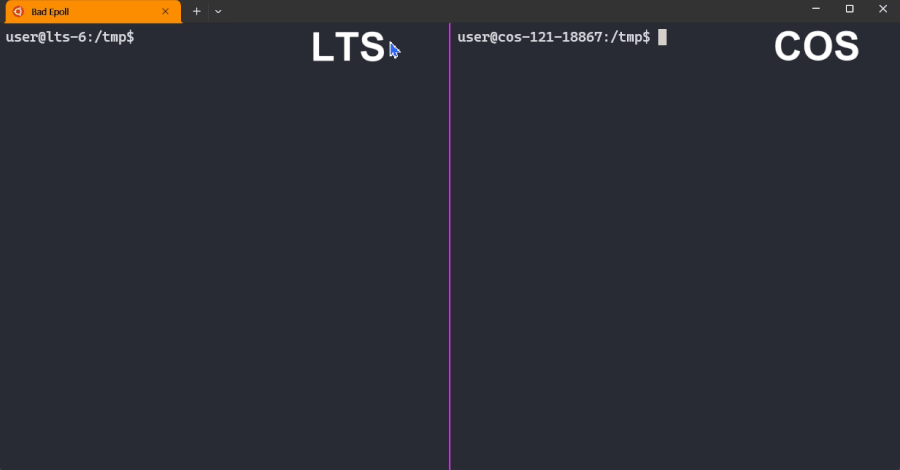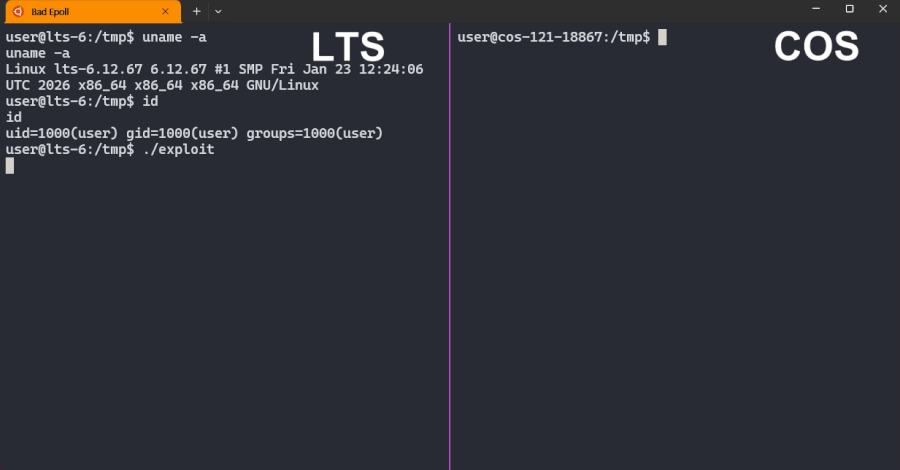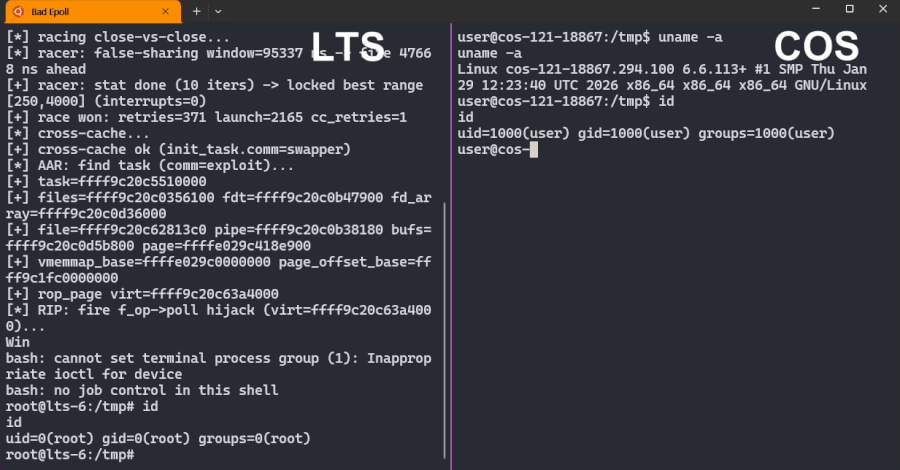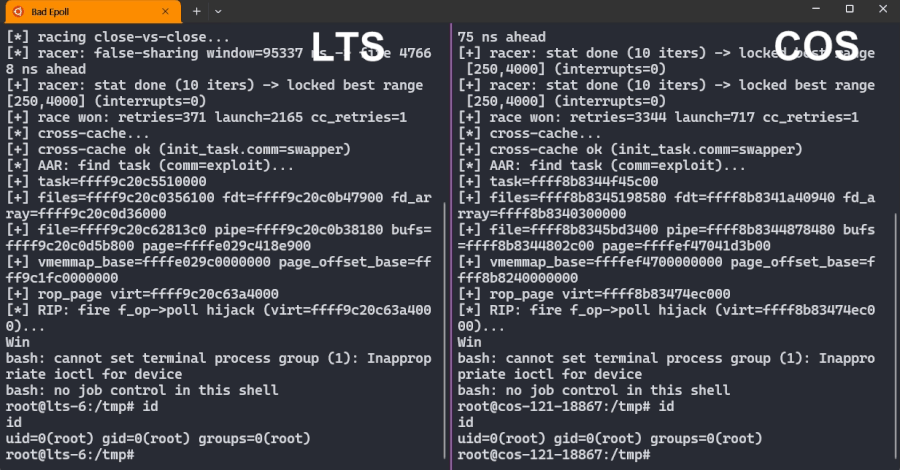
A privilege escalation vulnerability, identified as CVE-2026-46242 and dubbed 'Bad Epoll,' has been discovered in the Linux kernel. This flaw allows unprivileged users to gain root control over Linux systems, including desktops, servers, and Android devices. A fix has been released, making immediate patch deployment imperative to mitigate the risk of system compromise.

Carlos "Emérito" López Lovera
Cybersecurity

DirtyClone: Undetectable Privilege Escalation in the Linux Kernel and Its Implications

The DirtyClone vulnerability (CVE-2026-43503) is a privilege escalation flaw in the Linux kernel allowing local users to gain root access. Part of the DirtyFrag family, it undetectably rewrites executables in memory without leaving disk traces, complicating detection. With a CVSS score of 8.8, it marks the fourth critical Linux kernel vulnerability disclosed in the past six weeks.

Carlos "Emérito" López Lovera