Cybercriminals accessed over 170 Microsoft 365 environments by compromising ConnectWise Cloud Backup credentials, forcing the company to suspend the service.
Bitdefender has identified Midnight Mimosa, a malware campaign embedded in the firmware of budget Android phones that monetizes ads and creates zombie proxy networks.
Cybersecurity researchers have identified the P7 variant of the DarkSword iOS kit, which extracts keychain credentials, steals crypto wallet data, and executes remote commands via SpringBoard.
Threat actors are exploiting recently disclosed vulnerabilities in PaperCut software, specifically CVE-2026-81578 and CVE-2026-82078, to perform authentication bypasses and steal credentials. Attacks are targeting the education sector in the United States and Europe, impacting schools and universities.
A critical authentication bypass vulnerability (CVE-2026-82329) in JFrog Artifactory is actively being exploited to generate tokens with administrative access, compromising binary repository security and the software supply chain.
Ruby on Rails has patched critical vulnerability CVE-2026-66066 in its Active Storage component, with a CVSS score of 9.5. This flaw allowed unauthenticated attackers to read arbitrary files and escalate to potential remote code execution (RCE) in Rails applications, impacting image processing.
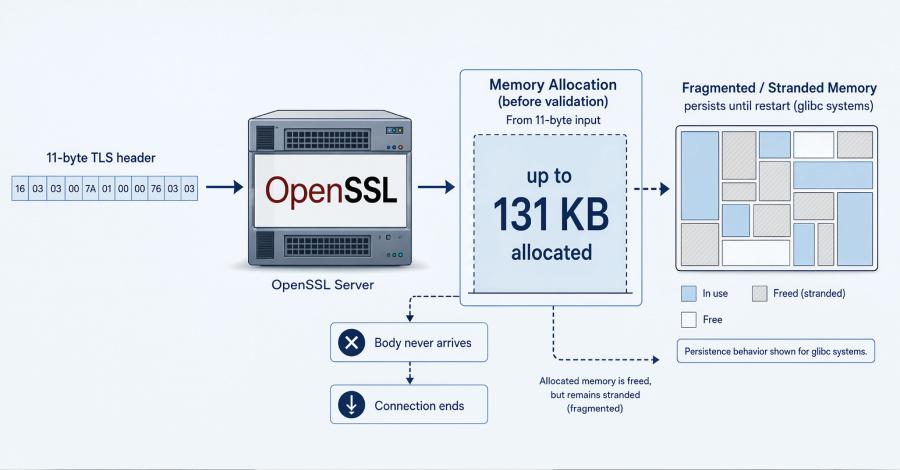
A critical vulnerability, dubbed HollowByte, allows unauthenticated attackers to induce a Denial-of-Service (DoS) condition in OpenSSL servers using a mere 11-byte payload. This attack can freeze up to 131 KB of memory per request on glibc-based systems, persisting until the affected process is restarted. OpenSSL implemented a fix in June 2026 without a CVE, public advisory, or changelog entry, creating significant challenges for security management and critical patch identification.
The Cybersecurity and Infrastructure Security Agency (CISA) has issued urgent directives to U.S. federal agencies to patch two actively exploited vulnerabilities: one in the Langflow AI agent development framework and another of maximum severity in the Adobe ColdFusion platform. Both require immediate mitigation, with a deadline set for Friday, highlighting the exposure to significant risks in critical AI infrastructures and government web applications.
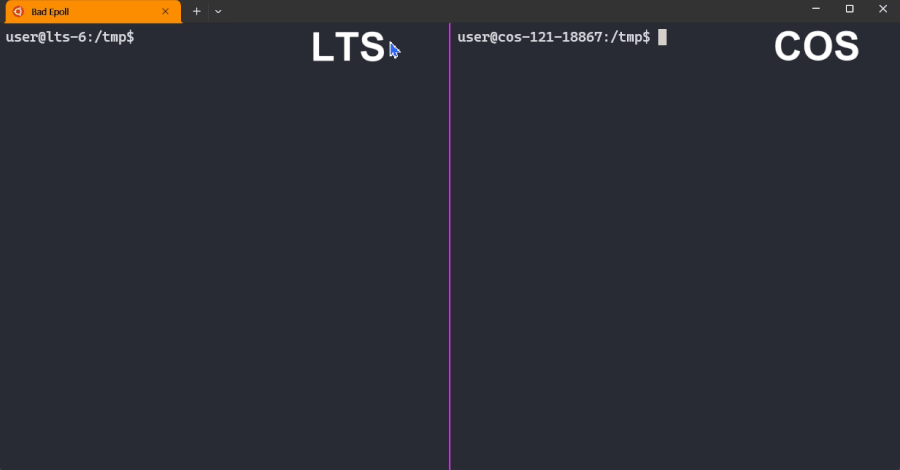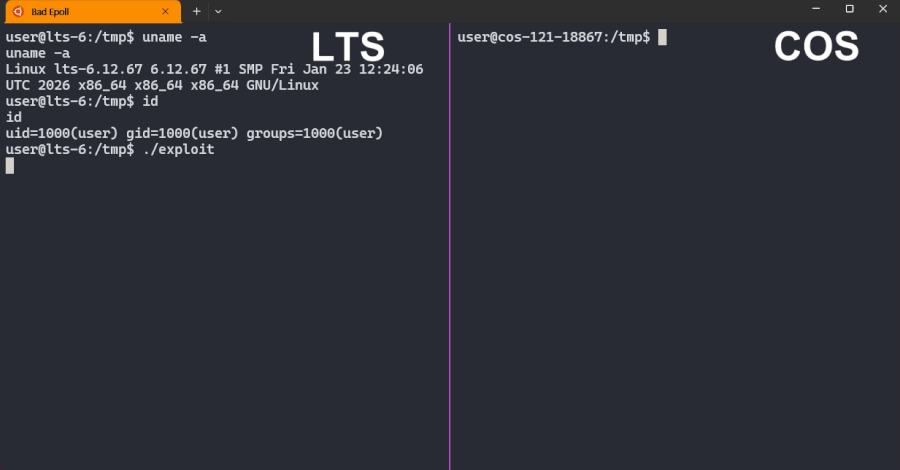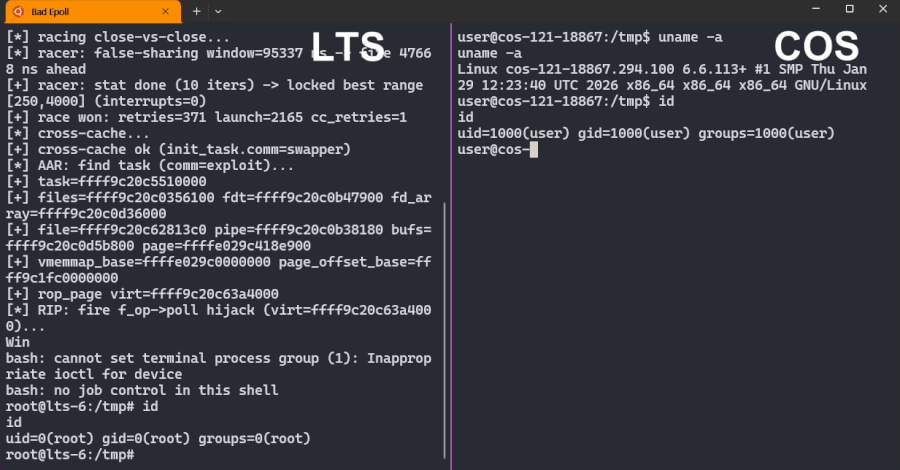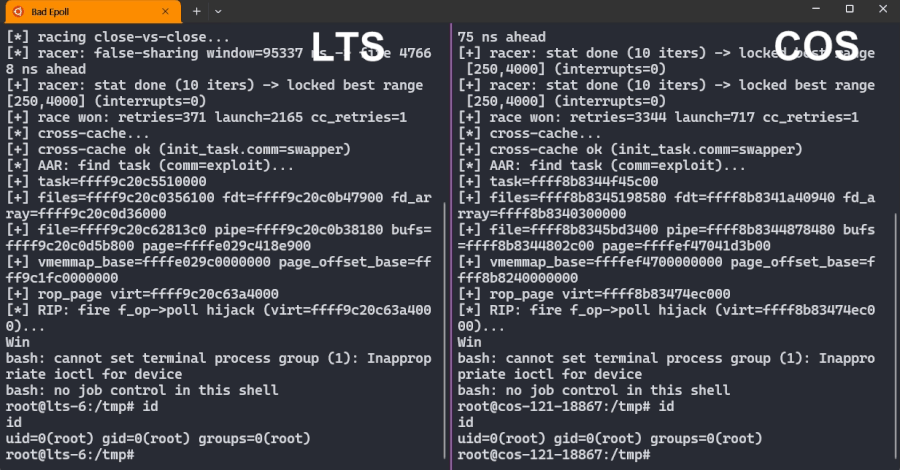
A privilege escalation vulnerability, identified as CVE-2026-46242 and dubbed 'Bad Epoll,' has been discovered in the Linux kernel. This flaw allows unprivileged users to gain root control over Linux systems, including desktops, servers, and Android devices. A fix has been released, making immediate patch deployment imperative to mitigate the risk of system compromise.
The Cybersecurity and Infrastructure Security Agency (CISA) has imposed a three-day deadline for U.S. federal agencies to mitigate a critical zero-day vulnerability in Check Point's remote access and mobile access VPN products. This vulnerability is actively being exploited by affiliates of the Qilin ransomware group, compromising the security of dozens of organizations and exposing critical systems to data exfiltration and operational disruption.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added vulnerability CVE-2026-28318, affecting SolarWinds Serv-U, to its Known Exploited Vulnerabilities (KEV) catalog. This high-severity vulnerability (CVSSv3.1 score of 7.5) is actively being exploited by malicious actors to cause server crashes, emphasizing the critical need for immediate mitigation in corporate and government environments.